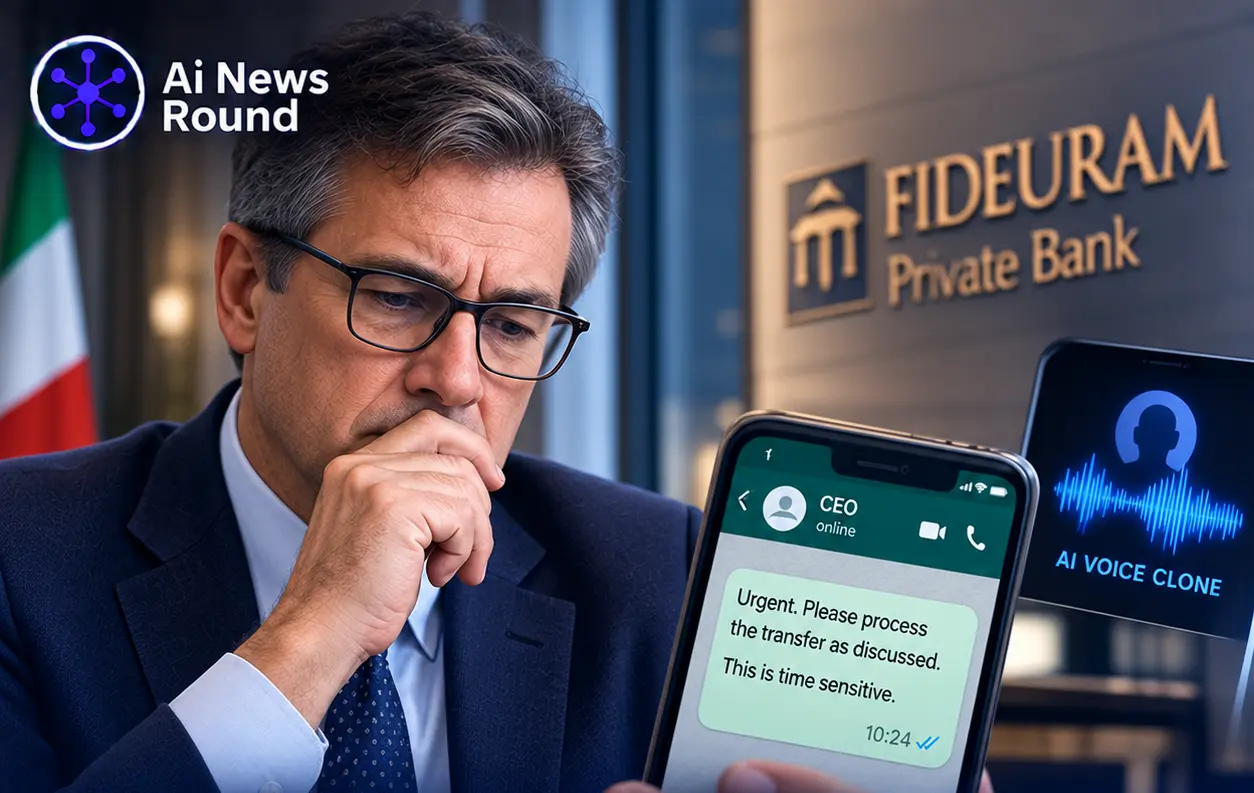
Executive Impersonation via Messaging and Audio Cloning
Cybercriminals executed a multi-channel fraud attack against Fideuram, the private banking subsidiary of Italy's financial group Intesa Sanpaolo, resulting in the unauthorized transfer of approximately €95 million. The operation was initiated when former Fideuram Chairman Paolo Molesini received a spoofed WhatsApp message appearing to originate from Intesa Sanpaolo Chief Executive Officer Carlo Messina. The message requested immediate assistance regarding a sensitive, urgent overseas transaction.
To reinforce the legitimacy of the initial request, Molesini subsequently received a telephone call from an individual impersonating a senior partner at prominent international law firm A&O Shearman. The fraudsters utilized artificial intelligence voice cloning tools to replicate the partner's actual speech patterns and tone, convincing Molesini that the transfer request had been verified by legal counsel. Convinced of the transaction's authenticity, executive authorization was granted to execute multiple international wire transfers.
Funds Routing and Asset Recovery Operations
Following executive approval, funds were routed through a complex network of foreign bank accounts concentrated in Hong Kong and mainland China. Internal anomalies were subsequently detected by bank personnel, triggering emergency asset-tracing procedures in coordination with international law enforcement authorities.
Cross-border cooperation between judicial authorities and financial intelligence units across Italy, Portugal, and China enabled the freezing and recovery of approximately €53 million. Specifically, investigators successfully blocked over €40 million in Chinese financial institutions alongside €13 million frozen within Portuguese banking entities.
Legal Investigation and Remaining Losses
Despite rapid recovery efforts, approximately €36 million remains unrecovered after cybercriminals routed the capital through intermediate accounts and converted the proceeds into undisclosed cryptocurrencies.
Milan-based prosecutors have launched a formal computer fraud investigation. Judicial sources confirmed that a foreign national residing outside the European Union has been formally placed under investigation. Law enforcement authorities clarified that neither Paolo Molesini nor other internal Fideuram executives are suspected of wrongdoing or under active investigation, identifying them strictly as victims of an advanced deepfake fraud scheme.
For more background on deepfake mitigation strategies and automated security risks, view our report on Google Gemini Entering Corporate Infrastructure and explore additional updates in our AI Policy & Regulation section.